

Traffic flow
Clients connect to a proxy IP; Gcore filters the traffic at the nearest PoP and forwards clean connections to the origin.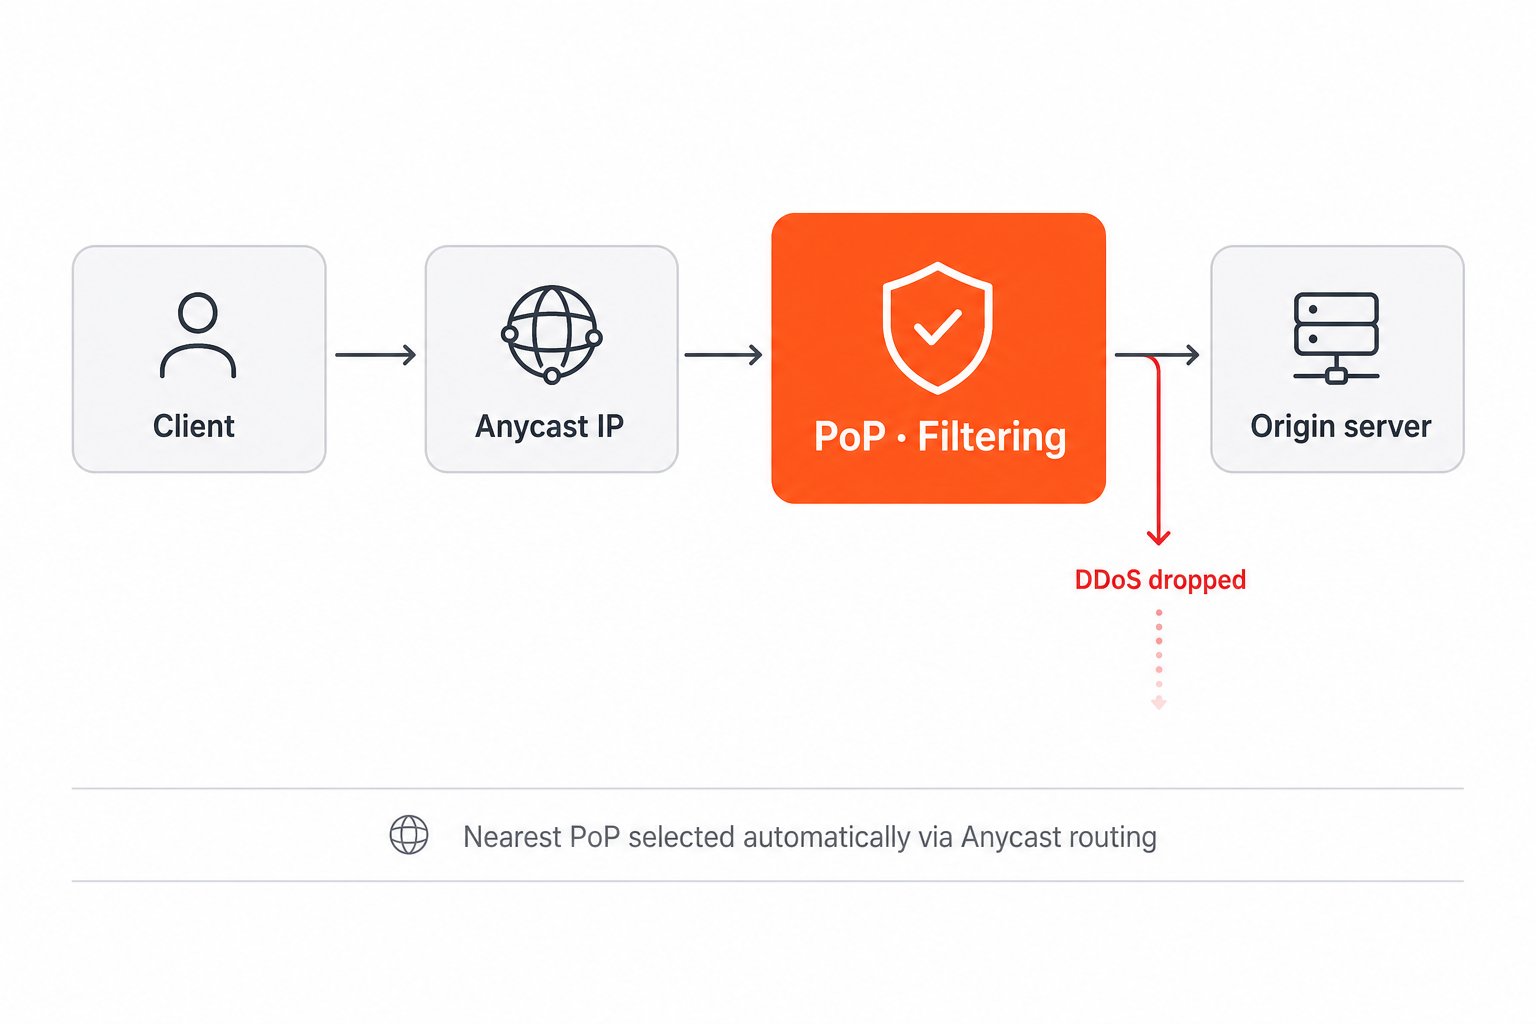
- High availability — traffic distributed across multiple PoPs removes regional bottlenecks and enables multi-terabit filtering capacity.
- Lower latency — processing at the nearest PoP reduces round-trip time and improves responsiveness.
- Simple setup — configured in a few steps without managing virtual machines or networking components.
- Efficient IP usage — multiple servers share the same Anycast infrastructure, so no additional transit or IP allocation is required per server.
- Flexible configuration — multiple applications and ports can be protected behind a single proxy IP.
Core concepts
The following terms appear throughout the Edge Proxy documentation.
Once configured, Edge Proxy assigns a proxy IP, starts filtering traffic immediately, and exposes traffic metrics in Traffic Overview.